
Other
Tech Industry Braces for Sweeping Changes as EU's Cyber Resilience Act Nears Implementation
MA
Mark Johnson
3 weeks ago
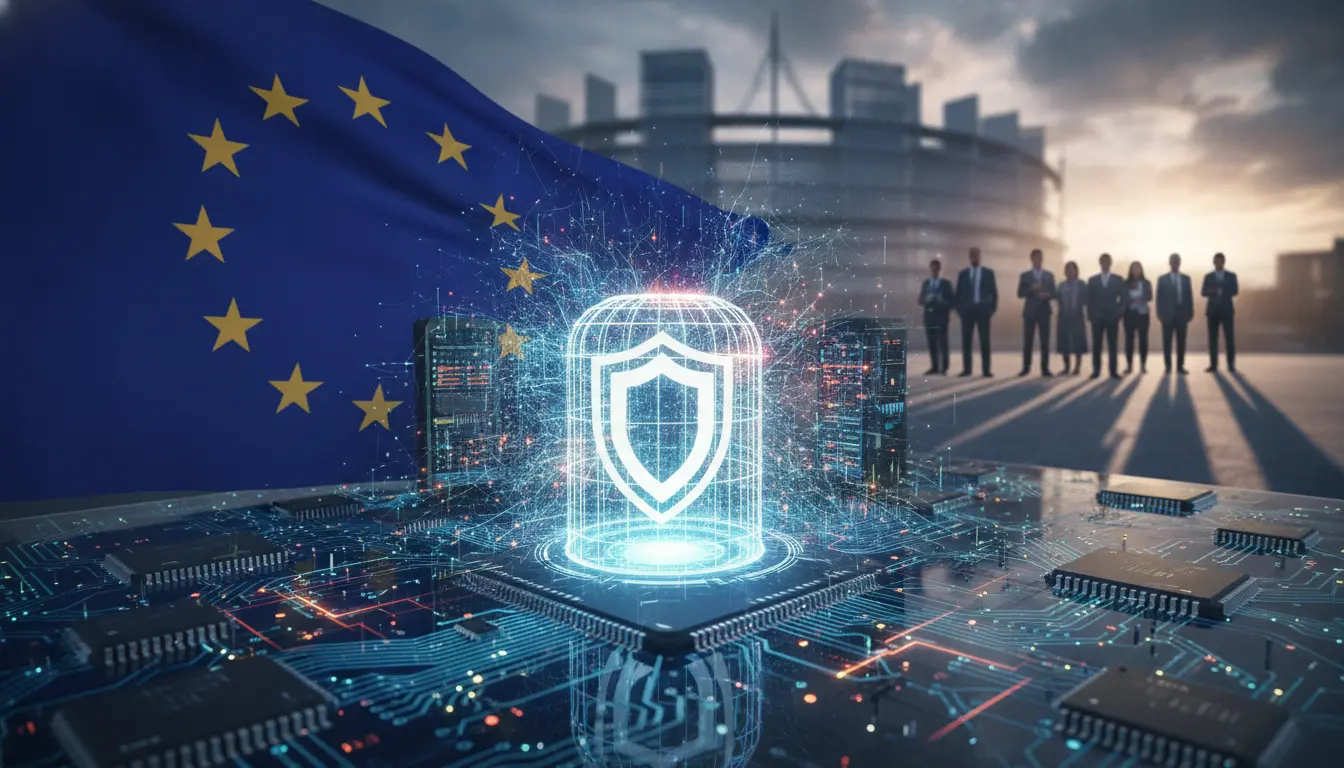
BRUSSELS – A new era of digital product regulation is dawning in the European Union, as the clock officially begins to tick on the implementation of the landmark Cyber Resilience Act (CRA). With the legislation now formally adopted, thousands of manufacturers—from global tech giants to small-scale gadget makers—are facing a multi-year sprint to overhaul their design, development, and maintenance processes to comply with some of the world's most stringent cybersecurity standards for connected devices.The act, a cornerstone of the EU's digital strategy, aims to tackle the rampant security vulnerabilities found in countless products with digital elements, a category that encompasses everything from smart refrigerators and children's toys to industrial sensors and software suites. For years, European regulators have warned that the proliferation of insecure 'Internet of Things' (IoT) devices has created a massive attack surface for malicious actors, posing a threat to individual privacy, critical infrastructure, and the bloc's overall economic security. The CRA is Brussels' comprehensive answer, shifting the responsibility for cybersecurity squarely onto the shoulders of those who place products on the market.At the heart of the legislation are several transformative obligations. Manufacturers will be legally required to incorporate security considerations into every stage of a product's lifecycle, a concept known as "security by design." This includes conducting rigorous risk assessments, ensuring products are delivered without known exploitable vulnerabilities, and providing clear instructions for secure use. Furthermore, companies must guarantee security updates for the expected lifetime of a product, or for a minimum of five years, effectively ending the common practice of abandoning software support for older devices, leaving them permanently exposed to new threats. The rules will apply to nearly all hardware and software sold in the EU, with only a few exceptions for highly specialized sectors like medical devices and aviation, which are already covered by separate legislation.Perhaps the most demanding and time-sensitive provision is the new mandatory reporting framework. Under the CRA, manufacturers will be compelled to notify the EU's cybersecurity agency, ENISA, and relevant national authorities of any actively exploited vulnerability or severe security incident within 24 hours of becoming aware of it. This rapid-response requirement is designed to enable a coordinated European response to emerging threats and to ensure information is shared quickly to protect the wider ecosystem. For many companies, this will necessitate a complete restructuring of their internal incident response protocols and legal compliance teams, a significant operational and financial undertaking.The road to the CRA's adoption was not without controversy. While many cybersecurity experts lauded the EU's ambition, industry groups and open-source software foundations raised serious concerns. Small and medium-sized enterprises (SMEs) warned that the high costs of compliance could stifle innovation and create insurmountable barriers to entry. The open-source community, in particular, feared that developers of free, non-commercial software could be held liable for vulnerabilities, potentially chilling collaboration. In response, EU lawmakers introduced several amendments in the final text to provide more clarity and flexibility, including specific carve-outs for non-commercial open-source projects and measures to support smaller businesses.With the final text now in place, the legislation will enter into force, and its provisions will become applicable in stages. Most of the rules, including the design and support obligations, will apply 36 months after entry into force, giving companies until roughly late 2027 to achieve compliance. However, the critical 24-hour reporting obligation for manufacturers has a shorter, 21-month deadline. This staggered timeline underscores the urgency regulators place on transparency and incident response. The impact of the CRA is expected to extend far beyond the EU's borders, exemplifying the so-called "Brussels Effect." Any company worldwide wishing to sell its connected products to the EU's 450 million consumers will have to meet these new standards, effectively making the CRA a de facto global benchmark for digital product security.
Stay Informed. Act Smarter.
Get weekly highlights, major headlines, and expert insights — then put your knowledge to work in our live prediction markets.
Comments
It's quiet here...Start the conversation by leaving the first comment.